
Passwords are a problem
Credentials are the main target of cyber criminals, because a username and password unlocks access to corporate systems, data, and IP.
Static 2FA is not enough
Two-factor authentication (two-factor authentication) was supposed to be the solution to weak passwords. Adding an additional challenge during login, MFA makes it harder for criminals to gain access with stolen passwords.
But…cyber criminals have become more sophisticated, intercepting one-time passwords, stealing hard keys, and so on.
Fact: All logins are not equal
Some login attempts are more risky: like ones from locations known for cyber espionage. Or, a user logging in from an unfamiliar device at an unusual time of day.
Trusted experiences require the fastest, simplest, secure login possible—emphasis on secure. That means a low risk login should be passwordless, fast, and easy. But a login flagged as high-risk should face serious challenges.
And it means never relying on a reusable password.
Introducing SmartFactor Authentication™
Today’s adaptive authentication has to be smart enough to evaluate the risk and context of each loginand adapt accordingly.
That’s exactly what OneLogin’s SmartFactor Authentication does.
Powered by OneLogin Vigilance AI, SmartFactor Authentication uses machine learning to automatically adjust authentication.
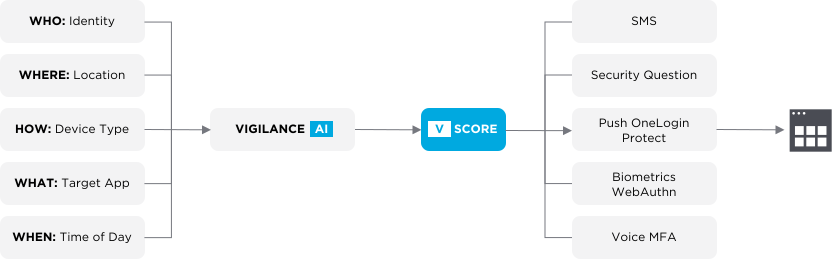
SmartFactor Authentication protect data
What does SmartFactor Authentication take into account?
- Location
- Time of day
- Device
- Target App
- Past user behavior
- Network reputation
- Device fingerprint
- And more
Powered by Vigilance AI™
What authentication factors does SmartFactor Authentication use?
- Certificates
- SMS
- Security questions
- OTP
- Email MFA
- Biometrics
- Voice MFA
Powered by contextual login flows