SmartFactor Authentication™
Prevent cyber threats with context-aware adaptive authentication
Detect and respond to high risk logins without sacrificing usability
Standard multi-factor authentication (MFA) uses static rules requiring users to authenticate every time they log into an application. However, this can impact the user experience and does not always effectively protect an organization from more advanced threats like spear-phishing and brute force attacks.
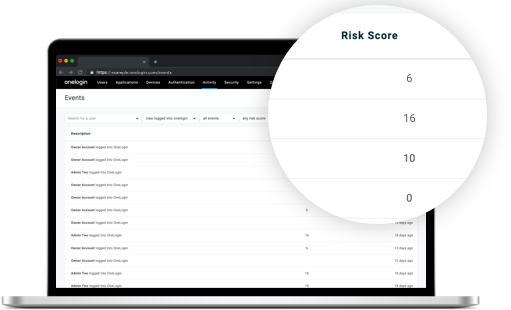
SmartFactor Authentication leverages our Vigilance AI™ risk score to dynamically adjust authentication requirements in real-time based on the level of risk for each login, balancing security with usability.
Dive in to learn more
Read our product datasheet for more information about OneLogin SmartFactor Authentication
How SmartFactor Authentication works
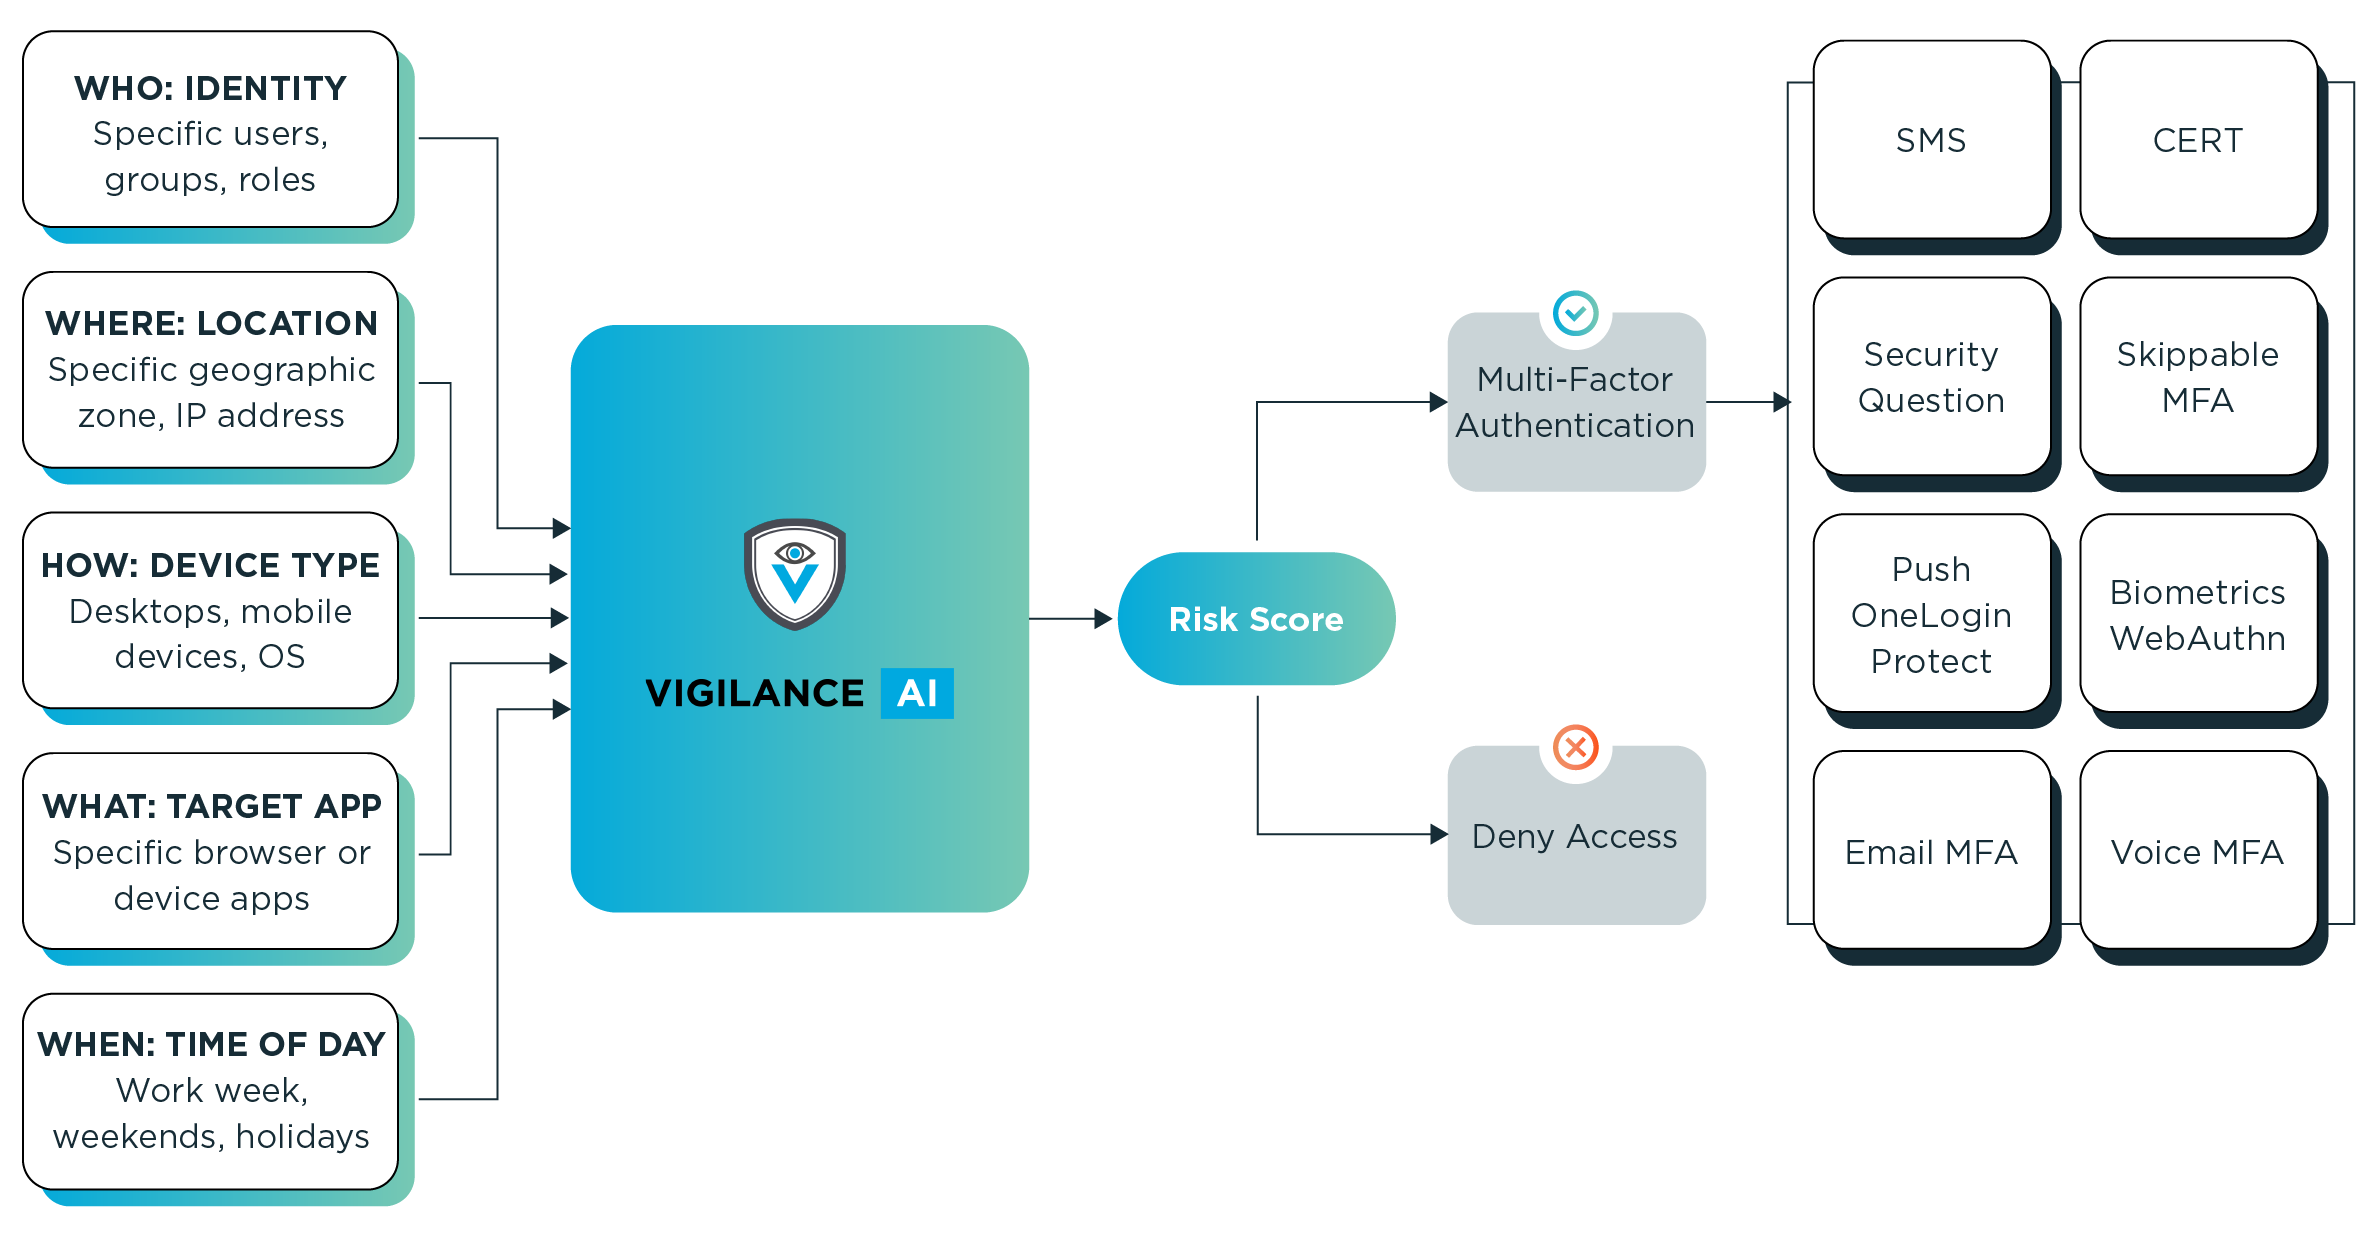
OneLogin’s SmartFactor Authentication uses machine learning to analyze a broad range of inputs, such as location, device, and user behavior, to calculate a risk score and determine the most appropriate security action to take for each login attempt. Depending on the detected level of risk, SmartFactor Authentication adjusts the number of authentication factors needed to log in.
Configurable Authentication Flows
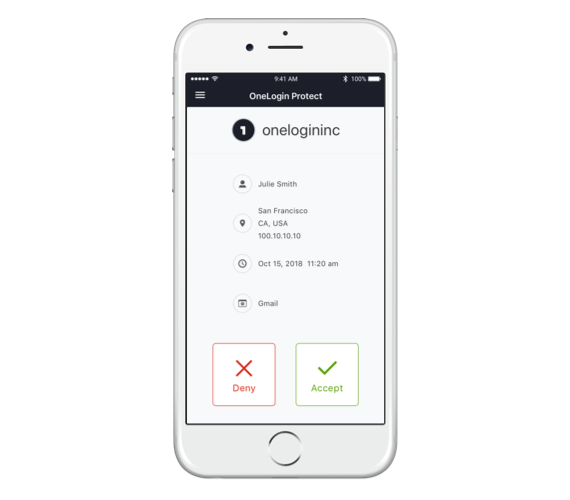
OneLogin lets you define authentication flows based on user policy to defend against brute force attacks, reduce account lockout, and enable frictionless logins for low-risk users.
- Enable passwordless authentication for users on a trusted device
- Check the user’s ID and device first and then, based on the risk score, prompt for an additional factor only if needed
- Use OneLogin Protect to remove friction by letting users simply respond to an MFA push notification on their mobile device.
Policy-Driven Access Denial
Sometimes it’s not about limiting access but denying it. OneLogin lets you create user or app policies that deny access under certain circumstances.
Compromised Credential Check
Protect against hackers using stolen credentials. When users attempt to create or change passwords, OneLogin checks their new password against a database of compromised credentials that have been stolen in large-scale attacks to prevent the use of stolen passwords.
Plays nicely with others